52:57 Webinar
A Darkening Landscape: AI, Friend and Foe of Cyber Resilience
In this webinar, we’ll examine a strategic framework that integrates AI-powered anomaly detection, immutable snapshots, and rapid cleanroom recovery—showing how to turn your data estate into an active resilience layer.
This webinar first aired on June 4, 2026
The first 5 minute(s) of our recorded Webinars are open; however, if you are enjoying them, we’ll ask for a little information to finish watching.
Click to View Transcript
Good morning, and welcome to our tech talk today called AI: today called AI: Friend or Foe of Cyber resilience? I am Scott Taylor. I lead the field solution architecture team for cyber resilience at Everpure, and really appreciate your time and everybody joining us this morning. I am joined by a couple of very special guests.
First is Matt Kimball. He's the vice president and principal analyst at Moor Insights & Strategy. Welcome, Matt. Thanks for joining us this morning. Yeah, thanks for having me, Scott Dietzen. It's great to be here. I also have Brad Tallman.
He is our director of product management for cyber resilience. A little bit of a partner in crime for me, actually, on the Everpure side. Welcome, Brandon. Thank you also for joining us this morning. Yeah, absolutely. Excited to be here. All right, so before we jump in, let's just have a quick review of what our topic looks
like today. And of course, it's no surprise because we have it right on the title slide here. We're gonna talk a little bit about AI, and AI is really reshaping that cyber landscape. It's helping defenders move faster, at least there's the potential for it. I think we're a little early in that, but we'll talk about that.
But it's also lowering the barrier of entry for attackers, and it's absolutely compressing the time that organizations have available to them to detect, respond, and DR. So I like to look at it as the collapsing exploit window that's out there today. But that shift is forcing a broader rethink of that topic of cyber resilience. So that question for, you know, not only vendors like Everpure, or analysts who are
looking at that broader market, but obviously our customers is, it's not how to prevent a ransomware. We're kind of at that point where I think, know, at least my opinion, if somebody wants to get in, they're going to be get in. But it's how do you keep the business running? How do you restore that trusted data as quickly as possible?
And then how do you recover with confidence, which is really important. You don't want to just recover, but how do you recover with confidence when something does get through? And that's why this conversation really matters. So Matt Kimball, you know, you wrote a great recent paper that makes the case that storage can no longer be treated as a, you know, a
passive defender, if you will, or passive infrastructure. It has to become part of that foundation of a cyber resilience strategy. So today, we're gonna explore that a little bit, both the market perspective, that's why we have Matt here, right? He sees a lot of things out there. And then Brandon's gonna be representing, of course, the Everpure perspective.
So what AI is changing, why has cyber resilience become that priority should CISOs and infrastructures leaders be thinking about? What do they need to do a little bit differently? So with that set up, are you guys ready to jump in? Let's jump in. All right.
So our first question, Matt, we're gonna go to you first. Mm-hmm. Let's start with this market shift that you're seeing, you know, kind of the reason behind why you, you wrote this paper. You make the claim that storage can no longer be treated as a passive target or a passive infrastructure.
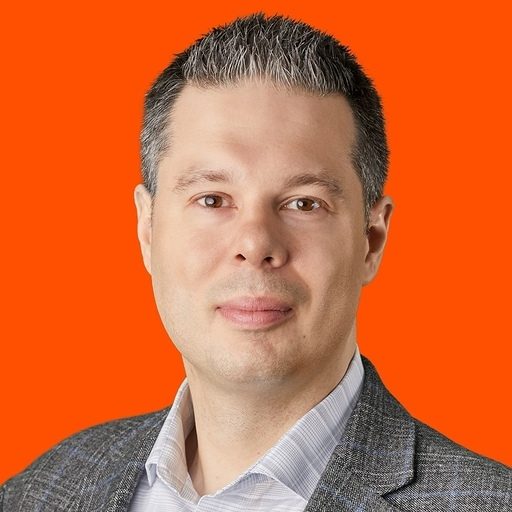
What has really changed in that threat landscape that has made you conclude that this is now an urgent matter? Yeah. Before we, before we jump into that, I just want to say, you FlashArray our, our profile pictures. I aspire to have Brad Tallman's profile picture as mine.
He has a rugged, cool look, and I l- you Both you and I, Scott Dietzen, I hate to say it, we look like nerds. Um- We, we do. Well, yeah. You know, I, I'm, you know, leading a solution architecture team. It's a requirement to look like a nerd for me, so.
Fair enough. Yeah. Good It's a really good question, by the way. So, and before I answer that directly, I'm gonna give you a little context to kind of my view of the world. So I'm an analyst at Moor Insights. Prior to that, I spent time in the vendor side as a technologist, and I spent time in the IT
side as a, as a state CIO for State of Florida and State of Oregon. And I say that because I've seen this from kind of all different directions, right? And I've seen the early stages of that threat landscape kind of emerging and it's gone to. But if you kind of look at kind of why, why storage can't just be this passive part of your IT and AI infrastructure anymore, I, I
kind of put it to, to three kind of buckets, and you hit on them a little bit. But the first is, is real simple, and I think everybody's seen it. The threat economy, it's just changed the shape, right? It used to be when you would hear about ransomware attacks and these, like, these scale ransomware attacks, it was nation states or it was groups of hackers that came, and
very sophisticated, that came together, and the purpose in many ways was more ideology than it was, than it was financial. This thing calls, called RaaS comes along, right? Ransomware as a service, and it lowers the bar, and it makes it very profit driven. And it goes from very sophisticated folks that are infiltrating and slowly,
stealing data to my mother texting me and asking me how she can, hijack, Microsoft Azure's website for profit, right? I say that jokingly, but that's the point, right? The bar has been lowered so low that ransomware, generating ransomware and, and ransomware has become fairly easy and commonplace.
That's the first. The second is ransomware, and it's kind of leading, leading edge. You know, as, as ransomware has become easier to, to build and to use and to, attackers, more sophisticated, they're starting to move down the stack. They're going to the data lakehouse, the, the data l- data layer itself, right?
Backups, snapshots, metadata, replication. Nearly half of the ransomware victims I've seen, lately They see this, where there are attempts to either corrupt or just delete backups to make it impossible and, and put the Pure Storage or the, the victim in a, in a, a no-win situation. And the third is related to AI/ML.
You hit on it. AI/ML is a tool, but it's a tool for good and, you know, as, as some cartoon character said, it's a tool for evil as well, right? It- it's, it's real, right? Faster, larger ransomware, shorter window to detect, shorter window to respond, and window to, to recover.
And so, you know, data-driven orgs, you know, and that's kind of every company today, thank you AI, are the richer likely or more likely targets. And I, I would say this, you know, the day attackers started going after backups and immutable snapshots, you know, those things you recover with, that is when passive infrastructure, and it became your last line of defense.
And if you can't have and, and if you can't have an ActiveCluster as your last line of defense, you're in a lot of trouble. And that's why I think, you know, as you look at storage, it just can't be a passive, player anymore. I agree, Matt. There's, there's actually
a lot to unpack there. I mean, first of all, you and I clearly have different mothers because my mother can't even text, let alone trying to figure out how to extort someone. So that's quite interesting. I, I also, you know, just want to hit on something there too.
Obviously, that, that barrier of entry is lowering, right? So you do have more people getting into this. I often look at it as, you know, you've moved from a, a technologist, or you called us nerds earlier, so you know, that nerd mindset almost to a business mindset. Yeah. And the tools have allowed people to do that.
Yeah. I do wanna make sure people know that the nation-state threat, the advanced persistent threats, they're still real. Sure. They didn't go away. Yes. Right? Like, we're not very far removed from a, a Pure public nation state sponsored ransomware, right?
So that's really still there too. And also just emphasize, like, we've, we've seen what you're talking about with customers. You know, we obviously have technology, that's why we're talking about this today, that can prevent some of these things, but when customers don't use that technology, we have seen exactly what you talk about, where they will go in, they will remove the protections
from the storage if you're not leveraging the right tools. So Matt, you know, you're describing here kind of a shift from prevention alone to really cyber resilience as an operational requirement. Mm-hmm. What does that change in how CISOs and other IT leaders, right, might be the CIO, VP of infrastructure, should be thinking about their priorities? Yeah.
I think the first is, you know, as you, as you mentioned, right? The, the model flips, right? I think a lot of organizations And, and by the way, to this day, a lot of CISOs, I say CISOs, but CIOs certainly, those that Let me actually backup. If you look at kind of, you know, storage and the cyber resilience intersect, you know
are organizations that if you kind of built out a capability maturity model, there are, there are organizations that are very far advanced and kind of get this. And, but the majority are still kind of figuring it out, right? And I say that as backdrop to a lot of CIOs I speak to still kind of look at the world through a prevention first, in a prevention, not only, but prevention
primary kind of lens, right? Prevention assumes you're keeping everybody out. And if you assume you're keeping everybody out, you've already lost, right? Cyber resilience assumes either they're in or they're gonna get in, and it asks, it forces you to ask and answer those hard questions around, can you keep running and
restore that trusted data you have to use Pure Rapid Restore fast, right? That's the first thing. The second thing is I see recovery as becoming more of a scrutinized pillar, right? It's not, do we have backups, but can we restore quickly, cleanly, at scale? And can we not only that, can we trust that RPO that we're s- that we're
restoring to? That's the second thing I would say. Third is, as I mentioned, right, detection is reaching the data layer. There is no doubt about it. And this is something that I think if, if I'm talking to SAP HANA and I do, as I talk to CIOs, this is something that comes up continuously, right?
Anomalo- anon- Having trouble speaking today. Anomalous rights, snapshot changes, you know, unusual admin activity. These are the things that usually start to show up first and the first kind of signals that something is going wrong. And we'll get into kind of AI/ML helps that, but these are the, these are the early signals
that you can kind of pull out of the noise. Fourth thing I would say is backup ends up becoming part of your security strategy. It's not just a, it's not just an operational thing, right? It moves out of that kind of IT ops silo, if you will. In governance, kind of becomes a board level auditable and kind of tested kind of
measurement for, what you're doing within that data protection routine and, building it into your security posture. And so I kind of would, I would anchor it, I, I guess, in, in kind of four pillars if, if you couldn't get to it, right? Data protection, detection, right?
So protect it, find it as fast as you can. When you find it, disaster recovery, recover as you can, and provide a real governance structure so that you're doing this and you're, and you're, by the way, you're testing against it, very, very frequently. And these all have to be anchored at the data layer.
Absolutely. And, and I want Bryan to comment on this but one point I, I just want to throw out, 'cause you kind of talked about the anomalous behavior. When we think about a lot of people focus on, like, scheming for ransomware kind of things. Mm-hmm. And I, I think there's a couple of challenges
with that view. First of all, like, ransomware tends to be polymorphic. It, it obviously tends to evade already existing tools from security companies that are constantly scanning the environment. Clearly they're not finding a lot of these things that are out there.
So really you have to start looking for, in my opinion, what are the behaviors that indicate that something is going on, versus looking for a particular file type or signature or whatever that might be. So I think that's an, it's an interesting point you brought up there. Yeah. And Scott Dietzen, you know, just adding to that a little bit, you know, there are
are types of ransomware, I mean, even when you get to, like, the lower level rootkit attacks, right, where they're virtually undetectable kind of through typical scanning techniques, right? They sit very low, they bleed data very, you know, very quietly and very small. And they don't last for hours, they last for days, weeks, months, right?
And these are, these are specifically the kind of activities. There is a signal, but it's a very subtle signal, and if you don't have the right tools, then you're not gonna number one, you're not gonna be able to find them appropriately, right? Or in the, in the, the time.
And you can go back, you know, over the last few years and you can see a number of government sites talking about nation states, and large corporations where these bleeds were happening, and they literally went undetected for months at a time. So finding those is, is critical. But that, going back to the data protection part of that too, right?
It's, it goes back to we can't assume, I know I've said this, but it's important. We can't assume that all of our prevention techniques, even with how much we've hardened infrastructure, you know, with Silicon Root of Trust and with all of these elements we've built, we've brought together, we can't assume that that is going to keep the attackers out. You have to look data first.
Not just data first, you have to look at all of those data stores you have that you're relying on to kind of rebuild from in the event that these ransomware are to happen. I agree. So Brad Tallman, let's get you pulled in little bit. When you look at that same market shift through our lens at Everpure, where do you see customers really rethinking
the role of data management? I mean, I mean, you know, Matt has, has, has hit on it pretty, pretty well, which is that, you know, STaaS as the active defender, right? Where these two, you know, security and storage are often separate parts of an organization, separate budgets, separate cultures even, right?
Separate recruiting streams. Like, they just, they don't always draw the same people, and so you have a different kind of mindset of, of, right, passivity versus, versus active. Security teams are active. They're o- they're often, you know, constantly investing, looking, monitoring, reacting, spending days, on incident bridges every week.
And I know that 'cause, like, my background is, is, is, you know, prior to this I, I ran a, a cybersecurity product team, for five and a half years at a Fortune 100 company. So I come from that perspective of an operator. And, you know, with IT teams, you know, generally y- you know, you might be on, an incident bridge, but it's probably related to some kind of availability incident.
Or you're doing a disaster recovery exercise, which maybe is over a weekend, know, very long, very slow process, where you're trying to sort of recover everything and prove everything out, right? And I think what we're seeing now is the, the threat window is closing so quickly that we actually have to be fast, right?
It's, it's really around not only the threat signals running through your entire environment, but really around how do you, you know, actively recover, and actively respond. And, you know, the, the closer you can bring the data layer to the folks who are monitoring your endpoints and your network, the, the better off you're gonna be. Because I mean, Matt hit on it.
Like, you have to assume breach. Like, this idea that it's gonna happen to somebody else in, in, you know, oil and gas telco or, you know, some, some government agency, it's not. It's, it's happening, you know, a huge number of small businesses are being hit, you know, every day. And so we really have to ensure that we're not
only, you know, building the right tools, then arming our customers, but also giving them the right strategy and, quite frankly, a, a cultural shift and a mindset shift. Because, you know, in, in the age of AI/ML, data has gravity, right? And, and a lot of the global economy is around digital delivery. And so we wanna make sure that we're protecting probably one of your most valuable
assets on-premises that has, you know, that especially with depending on what the attack is, like ransomware is, is one, but wiper attacks are another. Exfil- data exfiltration, you know, model poisoning. There's, there's so many, like, new threats around, and I think that we really have to make sure that we're sort of really nailing the basics around, you know, establishing
those security controls around your, your data management layer, continuing to invest in your perimeter, and really connecting your detection capabilities to your response capabilities into that data management layer. Hey, hey, Brad Tallman, can I just add something on that, to what you're saying? And it, it To emphasize your first point around kind of you've got storage folks and
you've got security folks and, you know, they're often very siloed. We did some, some primary research, some time back, qualitative in nature, right? So focus groups, where we brought in a bunch of IT executives from large, from small, from medium sized, and we were hitting on this discussion specifically, security. And it was shocking to hear the disconnect that takes place between not just security and
storage, but security and your more general IT group in general, right? Whether it's a server admin, a storage admin, network admin. I know it's collapsed or it, it's starting to converge a little bit, but those, those gulfs are still out there. And I, that, it's probably the first issue I would say a lot of organizations have to resolve, which is y- you can't operate
separately 'cause it hits to directly what, what you were hitting on there or talking to there. Yeah. You s I, I saw it most, you know, so I started my After the military, I started my career in financial services, and where I really started to s- watch the emergence of that cultural differences was in, like, the resiliency function versus the cyber resilience function
versus the IT function. Like, they, somehow they were all reporting to different leaders. And, and, you know, in financial services by and large, like they, they have historically had to do things, right? So, like that creates, you know, more budget to those, more seriousness with which people
take it, you know, compared to, say, maybe like a software vendor who, who doesn't always have to do disaster recovery. Um- and so y-you see a maturity there, but you also see a siloed nature. You see a very, like, it was, it would, it would drive me crazy sometimes where I would see some of the manual nature with which we would do things, like a BIA that was, like, 17
pages long and, like, it wasn't, wasn't connected to how a developer did anything. Yeah. And, you know, one of the, the great shifts I felt like over the last 10 years was around this idea of hiring a chief availability officer, and that really showed me w-where, you know, things like chaos engineering would bring cyber resilience and security, right?
Because not every availability incident's a security incident, but every security incident is an availability incident, right? Downtime is existential. So the faster you can recover from downtime, the m- the less revenue you're going to lose and the, and the more you're gonna delight your, your end user.
So, you know, really, the closer we bring these things together And it's not to say that everything needs to be fully automated. That's not necessarily what we're s- I think what we're advocating for. I think what we're advocating for is, is bringing teams closer together so that you're actually delivering a set of capabilities from a cyber resilience, from a security,
from an availability. You know, compliance is great, but we do compliance for a lot of different reasons. Like, at the end of the day, we wanna make sure that we're getting, you know, back in the game as fast as possible because, you know, Matt, you hit on it, like, things like dwell time now are 200-plus days, right, of threat actors, right?
You know, you're seeing the threat window close to under, under 30, sometimes 15, depending on who you quote. And, and I think we really have to start to automate our way out of, out of some of these things that have been, even in the security teams, have been historically manual, things like CVE, exploitation, patching. A lot of that stuff is hyper manual and, and very much more, more stick versus carrot, if
you will, when it comes to ransomware. Yeah. All right. So I'm gonna go back to, to our favorite buzzword, currently, which is AI/ML. And we think that AI is clearly accelerating the attack speed, but it expectations for something that Brad kind of just hit on a little bit,
automation and response. So where do each of you see AI/ML helping cyber resilience? Maybe Brad Tallman, if you wanna start. Well, I mean, I, I tend to I use this phrase, I've been using this phrase pretty, pretty, frequently r- lately. When people ask me about AI, I said, "You know,
I'm not an alarmist when it comes to AI. I just think it's machine identity with escalated privileges," which to me allows us to ground us in sort of what this means for us, which is that, you know, many companies I, like, I've worked at or I, you know, was a consultant for a little while, I would consult with, like, just sort of missed the analytics era.
And- Mm-hmm they, they Often what you'd see is just the lack of, of nailing the basics, right? Like, just your basic s- you know, se- secondary sites, you know, immutable snapshots your, around your hosts, you know, making sure that your network can't be, you know, really penetrated or DDoS. Like, there's just a lot of things that we just, like, didn't get super right, over time, despite some of the investment.
And so then you, then you're like, "But, oh, my God, if we have to learn AI," and it's like, to me, like, all you're doing is accelerating your own failure faster. And so I think what we need to do is not, is continue to invest in AI, but also to take a step back and say, "Do we have the right controls in place? Like, are, do we really, have we really thought about our own availability
requirements and our own cyber resilience requirements? Do we have You know, have we secured our data layer? Do we have the right guardrails in place? Like, that stuff to me is just table stakes, and the best organizations in the world are, have been doing that, and that's why you, I think you're seeing an acceleration and adoption of AI/ML.
But that being said, you know, AI/ML is also making the security teams better, right? Making the threat analytics and threat intelligence better, richer. The, the heuristics that we're getting from the various signals, the ability to, to take a S- a storage admin log and connect that to a threat intelligence, feed from, say, a CrowdStrike console, is, like, unheard of, right?
It reminds me of my time in, in, in counterintelligence. Like, it's just, it's so incredible, the ability of what we can do, but we have to be, we have to realize that the, the threat actors also have these things as well, right? And so we really need to get out of the, and I think what I hit on with Matt here, is the manual nature with which we respond.
You know, you, you would have a, you write a detection rule, and then you get a, a, a signal that goes to a, a, an endpoint and a SOC team, and then they respond, and then they get, like, 16 people on a bridge, and, like, Jim asks Steve if, if Alice knows what's going on. Like, the days of that stuff is, are over, right?
Like, it has to be automated. It has to be where you get a, there's an incident that takes place. It's already segregated from your production environment. You've already isolated it. You have Then your, to Matt's point earlier about, you know, what is your last known good clean copy?
You know, is it gonna take down our entire production environment? Can we continue to deliver services to our customers in the interim? That's the future, right? And it has to be, right? It doesn't, doesn't remove people.
It actually makes people super important, in my opinion, right? Putting people in the loop of your response is super important, but not when they're the bottleneck. Exactly. I think we've been talking recently a lot about human speed versus machine speed. And so, I, I'd heard something back at RSA where they said it's, it's impossible going
forward to have a human in the loop when you're talking about, like, the automated response, but you want, like, a human on the loop, is the way that they phrased it, right? Mm-hmm. So having control, having, you know, purview over what's going on, but you, you kinda need to be able to fight machine speed with machine speed.
Matt, what do you think? Well, I think the real value of an analyst is to repeat everything you said in different words. So let me try and do a good job. I am, I am fully on board with, with what you're saying. I think when I look at kind of AI as it relates to cyber resilience, Brandon, you
this really well, you know. It's, AI/ML, AI/ML's kinda lowered the barrier. We already talked about that, the attacker's barrier. So, you know, for, for organizations, using AI in your cyber resilience strategy is stakes, right? You, y- it's a, it's a bare minimum.
If you're not, you've lost, and you've gotta, you've gotta kinda figure this out. But I think what And also to what you said, I think the two biggest gifts I see, maybe three, as AI/ML relates to resilience is- Time, right? When you kind of when you, when you think about kind of data layer, kind of, surface anomalies, kind of, you know, or I should say data, data layer attacks and
kind of anomalies being surfaced earlier, you know, the ability to move faster is always better, right? It can be the difference between an incident and a ransomware, which I think is a big deal. It also, as you said, it sharpens the response loop. If you can pull out the Jim talking to Sally talking to Steve talking to Mary, if you can
remove that, and you can kind of feed your platforms and drive those automated playbooks, in a, in a, you know, a shorter timeframe, you're, you're, you're shortening that impact window considerably. I would say on the, the human in the loop, I agree, you know, human in the loops can't be there, but or, you know, you eventually have to rely on automation.
I would caution organizations, you know, there, there's still a human element to this. While we are relying on these tools to operate in an automated fashion, the policies, the creation of playbooks, the testing of those playbooks on a regular basis, you know, not in a planned fashion, but kind of really, you talk about chaos, in kind of a chaotic fashion to really assure your cyber resilience in an organization, I think that's
all critical. AI is the underlying it's, I guess, the underpinning to all of this, but, you know, the way you operate, the discipline you, you, you, you exercise as an organization ultimately is going to be what matters, right? It's how you use that AI capability. It's not AI itself.
Yeah, I agree. Absolutely. And I think I was just gonna say, I think, Matt, that's the human on the loop that the, the individual was trying to term. Yeah. You know, we're, we're making up all, all these new terms as we go along, but yeah. It, it's so another interesting correlation I've heard from somebody, which is, you know,
kind of AI/ML in the coding space, if you, if you think about it as another layer little bit, like we're not typically writing in machine code directly anymore, right? We have higher level programming languages. The next higher level programming language is AI/ML, and I think we have to maybe think that for the security context too.
It may not be somebody, you know, directly typing the keys on the keyboard to respond to something, but all the things that you just outlined is where the human now, you know, is able to extract abstract themselves a little bit higher. Can Just adding one thing to 'Cause you, you brought up something really interesting in there, Scott Dietzen, and that is, you know, one of the things I do see as I'm
Enterprise organizations is security is still a very, is a, still a fairly specific kind of discipline within the organization. But I'm finding as, especially as AI/ML comes into play in, in enterprises, that role of specialist is really starting to blur, right? I mean, compute specialist versus network specialist versus storage specialist.
I think somewhere where AI/ML really helps from a cyber resilience perspective is IT generalists, who are smart folks who know how to do a lot and can, can kind of understand higher levels of, or higher orders of, of thinking and critical thinking, it allows them to be more effective as it relates to kinda driving, you know, cyber resilience, I guess, if, if you will, across the organization.
So it, it kind of opens up the number of, of folks that can contribute and be significant in driving cyber resilience across an org. Instead of saying, "It's just these four people. It's just Jim, John, Mary, and Sally that are gonna be able to kind of, you know, drive, drive and manage these environments," it, it allows a, you know, it allows a lot of smart
folks that might not have that same depth of, of, domain experience or knowledge to, to contribute to the equation as well. It, it's just like we're talking about for, you know, the adversaries, right? We've, we've kind of democratized access a little bit for them. Yeah. The same thing for the IT practitioner.
Yeah. Let's look to the future for a little bit. You know, that's always good. I'm sure everything you guys are about to say is absolutely gonna come true. But, you know, Brandon, let's go back to you. If I'm If you're looking ahead, you know, let's say next 12 to 18 months kind of thing,
what do you think is gonna separate organizations that are truly, truly resilient from those that are still relying on kind of outdated theories and outdated operating models? It, you know, you have to any of the, the defense in-depth tools that you have that are not connected to what I think is the most important layer, which is where your data
is, like if any, any organization that is not connected to those things is gonna those are the ones that the threat actors are gonna go after, right? It's, it's, it's the reason, you know, it's the reason why we've, we put, you know, locks on doors, right? It's, it's not to, it's to keep the bad, the, the bad guys out, right? So I think the, the more that you neck not,
not go out and buy new tools, I can tell you that as somebody who, who operated like literally every vendor in the space. I worked at a very big company. I had all the tools. The thing I didn't have access to was the storage layer, which is why I'm now working at Everpure, right?
Is to help build that future for, for, for our customers. But work with your vendors, because I think one of the, one of the, the benefits from my perspective of, of having been a partner, having been a buyer is that s- is that our account executives and those, and, and SEs for, for, you know, Everpure as well as for our security partners, I can tell you, like, they don't stop, right?
They, they are there. They're on the incident bridges sometimes with you. Like, work with them to architect the best solution for you, right? Like, don't just, like, go off and think like, "Okay, I have like, I have a very s- finite budget.
I have to then get all these things connected." You know, we're You know, for instance, Everpure is very much here. We have a lot of reference architects. Like, we, we love I mean, myself and Scott Dietzen, I mean, I'll speak for Scott Dietzen just 'cause I, you know, I, I, we share a similar mindset.
We would love to come and talk to you about how to architect this stuff. Well, right? So think about that. Like, you're not here on your own, right? I think one of the things that you said, Scott Dietzen, was, you know, what is that next level of abstraction, in terms of AI/ML?
Like, it is passion. It's human passion. It's the fact that we care about this stuff, and we care about our customers, and we care about doing the right thing. That's the wonderful thing about cybersecurity, is that it brings people who, who wanna do purpose-driven work. I, I truly believe that, and I think the more that we can collectively as an industry come
together You know, of course we all have You know, there, there is competition, obviously, in what we do for our customers, but I think as an industry, we have to be transparent about how to, you know, m- meet the future, right? Because if we're doing this in silos and we're constantly saying, you know, again, sometimes vaporware out there in terms of what, what's real and what's not, like, we have to be
intellectually honest, right? Because, like, the ransomware only have to be right once. We have to be right 100% of the time. The more that we work together, the more that we collaborate, the more that we sort of push, you know, the private sector to work with the public sector, the more that we make this
stuff accessible for small businesses, not just major enterprises. And, and honestly, quite frankly, the more we talk about this in, like, plain business language, 'cause at the end of the day, we're preserving revenue, right? Like, we You know what? We have to get out of the business of, like, you know, security teams constantly going to
the board and using fear as a driving factor for how to get investment, right? You get investment because you preserve revenue. You get investment because you, you preserve customer, from, from attriting, right? Because you're, you're, you're increasing your uptime, and you're delighting your customers that way. Sure.
Are there a lot of ransomware out there? Absolutely. But, like, the idea that, like, we need to continuously invest in security from a fear perspective is only gonna work so far, and at the end of the day, you're gonna fatigue your, your executive leadership and your, and your, and your governance body, just fatigue them. Like, I saw it.
I've seen it a, a number of times. So we have to get to this place where we are, we are thinking as business leaders, 'cause it's ultimately what we are, about this critical business objective, which is to secure the organization and secure the data layer. Yeah, I think you, you had a lot of great points in there.
You know, you and I talk, and I think Matt does too, to a lot of security leaders, and it's interesting. They do not get a lot of time with boards or other executive leadership, right? I think I even saw an article recently. It's like, oh, CISOs have a C in their title, but they're not treated like other C-level
individuals in the company, and I think it's exactly what you're talking about. They go in, and they talk about, you know, number of CVE mitigated and a little bit more technical speak, and they don't talk about things like, you know, revenue disruption and how do I preserve revenue, right? How do I remove that customer attrition?
How do I keep us from, you know, having class action lawsuits and other things? So I think the way that we as an industry speak to our boards, to our executive leaders actually matters, and we've gotta talk in their language. We can't expect that they are going to be security experts. We have to meet them where they are.
The other thing that was kind of interesting, Brad Tallman, you know, back at RSA, there were something like 600 vendors on the show floor, I think. Something crazy. I mean, it was massive. And I went around and talked to not all 600, but a good bit of them, and, and one of the things that I saw was like, so how are you different from this person that's right next
to you and the other five people that said they do the exact same thing? Like, you know, there's so many tools out there. First of all, I don't think all of them are gonna exist in the next, like, three to five years. I think that show floor looks a lot differently.
But you can't get enamored with the tools or a whiz-bang kind of feature. That may or may not be the thing that saves you. Sometimes it's just the right controls in place. It's just doing the basics. It's just thinking through that architecture, like you said.
So I think a, a lot of great points in there. Matt, let's go back over to you. Look in your crystal ball. Yeah. What do you see? Yeah. Again, as an analyst, my job is to take everything you guys said and make it sound different somehow.
Y- y- your point A couple things, I wanna hit on before I, I dive in. Scott Dietzen, your point about the, what separates, you know, you from the others vendors that say they do the exact same thing and, and organizations becoming enamored, I forget what the number is now, but there is some crazy stat around the number of, discrete, security solutions that the typical enterprise deploys, you know, across,
across the organization. Crazy number, and they all kind of run siloed, right? If I am an IT person or if I'm IT If I'm a, a CISO, I'm a CIO, and I'm thinking about kind of building broad, kind of resilience, posture, the first thing I'm doing with all of, you know, with all of the kind of, options that are out there for me to buy from, I'm looking
at my Pure Storage environment first, and I'm looking at, you know, the openness of that and the openness of tools to connect. So going back to Brandon's point around connectivity, right? All these tools are great, but if I can't tie all of these security platforms I have to the most important thing that's sitting inside of my organization today, my data, then those
tools are for naught, right? So I'm looking for openness. I'm looking for connectivity. I'm looking for partnerships that might exist between, you know, if Everpure is my, my storage platform, Everpure and those solutions providers to truly provide that integrated,
capability, right? The other thing I would say is from a f- Y'all, y'all both hit on kind of the revenue impact and customer attrition. That speaks to something I think is even more important to, a company, and that is your brand, you know? That is the worst You know, brand suffrage you get from having a huge outage is causes more long-term damage than a temporary
dip in, in revenue or customers complaining to you. And, you know, it's a I think it's something when I'm thinking about, you know, how I'm going to protect my organization, the first thing I wanna do is make sure that, forget about 18 months from now, five years from now, people still have confidence and faith when I, you know, when I am presenting out my products and services to them.
And if, you know, the headlines are filled with, you know, Matt Kimball, you know, suffers yet another ransomware, and you know, X amount of customer data- I am concerned with losing a few million dollars, and I'm more concerned with, you know, that huge potential market saying, "I'm not gonna use that company because, you know, I can't Trust what I'm, what I'm getting from them." Um- Yeah.
So- I was just gonna chime in really quick, and I'm gonna steal a little bit of Brandon's thunder, 'cause, you know, as a product manager, he likes to say we ship trust. Yeah. And I think that's really important. You know, what gets the headlines is that initial revenue disruption, but we like to think of cyber resilience as capital events. Mm-hmm.
And the data actually shows, right, your long-term market capitalization will be negatively impacted over the long term. You will underperform your peers, right? You will underperform the market when you have one of these events, because that Trust Center really erodes.
I think it's a great point, Matt. Yeah. So I think, I think going you know, if you look in 18 months into the future, I, I, I don't think the dividing line between, you know, those who are successful and those who aren't are going to be what tools you've selected.
I don't think it's gonna be kind of how much money you've invested and how much those CISOs or the security folks have scared, you know, their executives or the board to get more money out of them. I don't think it's, it's about funding and tools. I think it comes down to organizational discipline.
It's something I hit on earlier, right? It's the operating model you have in place and your discipline in executing against that operating model. And it's so, and those are it's two it's important to kind of, to, to, to tease those two apart, right? Again, you can have the best tools in, in the world, you can have the best operating model
in the world, the best set of, you know, procedures and processes and, and, and, and notifications that go out to users and, and IT folks. You can have all of that nailed down, but if you're not executing discipline and actually, you know, utilizing this operating model, then it means nothing. So deploy the right tools, have the right operating model, and have the organizational
discipline to enforce everything that's built into those procedures and processes. I think that's a big one. And, and Brad Tallman, you hit on everything else, right? Silos, if you haven't kind of bridged the silos, you're in trouble. If you haven't looked at that data layer, data layer as being active, you know, you're
not starting from the right, you're not at the right starting point, or you haven't begun at the right starting point. And the other thing I would say is, the, the, the folks that are gonna be successful 18 months from now are the folks that have, not only kind of gone from we're creating backups, but we've, we create backups so we can actually prove and we can recover on a regular
basis from a variety of ransomware, and we can do it quickly, and we can do it cleanly. Continuous testing, not some annual checkbox that you can go back to the Yeah, we did this." And I'll stop there. So Yeah, and I think really using your resources in the best possible way, and start with small teams. You know?
Like, start to focus on the stuff that matters, right? Like, managers of managers of managers telling managers to do things, like, like we're, we're That is going away, right? Mm-hmm. And, and AI/ML is accelerating that, right? Like, like we, we need working leaders.
We need people who are closer to the work who understand how this is gonna happen, because the farther you are away from that data, data layer- Yeah the farther you understand what, what's missing today. So spend time in the field, right? Spend time, you know, inside of, of, you know, your teams that are that close to it.
And look for the gaps and say, "Are they operating model gaps? Are they cultural gaps?" I, I'll be honest, I think a lot of it's probably not technological gap, right? Yeah. I think it's cultural, right? And I think it's maybe even business model gaps, but where you're, you, you don't it's not that you don't have the right capital.
You're not investing that capital correctly, and you're not removing sort of the, the more manual processes, like the, the homework checkers, as I used to call them in my old job, or, like, the hallway, the hallway monitors, right? Like- Yeah we y- you can automate compliance. Like, you know, like, spend, spend the time in the areas that you need to, you need to focus
in on, right? Those things are already important. We're not saying that any longer. What we're saying is that, like, the days of, of over-investing in hyper-manual things and people sort of sending emails about, about meetings to set up, set up meeting Like, the threat window's too, too closing too quickly.
Like, we need to focus our efforts, and we need to focus our resources because, like, it's just, I think it's just too important. Because the customers of our customers now matter, right? Like, it isn't, it isn't so much that, like, somebody's gonna get upset with, you know, Matt Kimball Inc. Well, if Matt Kimball's Inc.
Delivers infrastructure to a hospital, and that hospital has an application that a nurse puts data into, who is that patient gonna be upset with? Matt Kimball Inc.? Maybe, like, if they understand how that works. Right. But they're probably gonna be mad at that nurse.
That's right. They're probably gonna be mad at that hospital chain. Yep. And it's just gonna and maybe eventually it will get down to Matt Kimball Incorporated, right? So at the end of the day, like, the customers of your customers truly matter because at the
end like, s- it's a small business owner that's processing a loan with that bank that, that they do business with, that they trust in their community. It's that nurse that they trust is gonna th- is gonna put that information in correctly so that their kid can get an MRI tomorrow. That's the seriousness with which we at Evergreen take this role and responsibility,
and I think that's one every, that every CIO and CISO needs to take as well. I love that. And I, I to what you're saying, I think, you know, looking 18 months from now, you know, you're talking about kind of, a resilience first mindset. I think if you have any, a, a, a prevention first mindset 18 months from now, you've kind of y- you're, you've lost, right?
And frankly, you kind of deserve what's I joke about you deserve what's coming, but, to you. But, but seriously, if you s- if you still have that cyber resilience first, and you're kind of, you're realizing mid-incident that, you have not tested those recovery plans, you have not, you, you've not kind of taken the right approach. You had you know, you put together all of
these kind of, these plans, but you haven't executed them and you haven't kind of continually made your organization better- You know, y- you kind of get what's coming to you. This is a Anyway, yeah, I'm beating the dead horse- Yeah Brad Tallman, I'm sorry. You, you, you build the ark before the floods. Yeah. I like that. Th- this is also so- something that's not
known, or, not, not known at this point, right? I think- Yeah y- you know. Yeah. We've spent a lot of time, you know, over the past 15, 20 years talking about things like disaster recovery Hey, the flood, the hurricane.
You know, you mentioned you were state of Florida, so I'm sure you talked about hurricanes- Oh, yeah tornadoes, whatever, and the reality is that those threats don't happen that often, right? It's not that they don't, so you need to be prepared for them, but you're not opening, I like to say, you're not opening your favorite news reader every WEKA and seeing that, you
know, a hurricane blew over Matt Kimble- Leake's data center, right? Right. But it's very likely that you're gonna open that same news reader and see that Matt Kimble Leake I- we shouldn't use your name, Matt. People are gonna think poorly of you. Yeah, I kinda like Matt Kimble Leake at this point. But Matt Kimble Leake- I have to tell you.
You know, we'll, we'll, we'll come up with another name. But basically, that, that organization has been hit by some kind of cyber event. That is, that is a weekly occurrence that those things are in the news. So this, this should not be ignored. Obviously, we know security professionals know it, but it goes back to how they talk
their, to their boards and executives. Those people can't ignore that risk anymore either. So we talked about a lot of good things, and this is kind of our last question for today. And Brad Tallman, I'll start with you, that way Matt can just reiterate or restate what you say.
Mm-hmm. But what do you recommend that CISOs do next to improve their cyber resilience? Test. Gain the confidence in your recovery today. Don't wait. Do it this weekend, you know. Like, literally go and just figure out who If you don't know, fi- go figure out who's in
charge of your disaster recovery testing, and say, like, "I wanna look at our, disaster recovery plan," right? Start there, right? Read your own disaster recovery plan, and then say, "Could you recover it?" to give example of, of how important this is, so there was a, there was a, a customer of ours, in March experienced a ransomware attack where the threat actor was completely
authenticated and wiped all their data, 80,000 endpoints gone, right, immediately. You know, the, at this point, the executives are completely concerned that they cannot recover. We were able to then come in and use our SafeMode technology to train a customer engineer in 30 minutes to recover from snapshots, right?
So I think that the, the complexity in, in the recovery process is usually in the technology that you've, you've bought or, or the, or the engineering that you've done on top of it. The complexity should not be in how you actually recover a thing, right? And I think we're proving that with our, our own technology and our own processes. But I think if you're an executive and you're not, you're not certain how everything works,
I think get really close to that work, right? Because that's the stuff that matters. That's the stuff that you're gonna report to. So, you know, figure out how to bring your, your, your security team to a disaster recovery test if, if they're separate, if, or your DR team to a security incident, and figure out how you can
bring those things closer together, and then what those gaps are, and invest in those gaps. Because it ma- like I've said, and I'll just repeat it, like, downtime is existential at this point, and the longer you hold on to traditional ways, you know, the l- the more obsolete you're gonna ultimately become in, in the next 18 months. I agree. Matt, what's your closing thoughts here?
What do you recommend for CISOs? I was gonna say test. No, I'm just kidding. Um- It's, I'm gonna Yeah, I think the first If, as I And I, by the way, this is, these are conversations we have quite a bit. The first thing I do is I say, you know, sit down and understand kind of where you are as
an organization. I think the testing is great. I think a lot of, but a lot of organizations kind of go into these, these exercises believing that they are in a certain when they're actually in a different and when they came to that conclusion of where they thought they were from a kind of cyber resilience or a, a prevention and resilience perspective, these were internal assessments they're doing.
I look at a company like an Everpure and Everpure's partners, and when I was a CIO, I loved my folks. They were the smartest folks in the world, and I, you know, I wanted to I would, I would bet my life and my career on them. But if I wanted an unbiased opinion, I went to an outside source to come in and give me the ugly truth, right? Somebody to tell me, you know, "My baby is
ugly, and this is why it's ugly." right? I mean, I guess the examples I'm using or the metaphors I'm using are not the best today. However, what I would say is run that STaaS assessment and use an outside source to understand where your real gaps are, both from a security perspective, but more importantly from a disaster recovery perspective, right?
You know, it's a understand, like, to get from, from incident to, restoring operations, where, where are you really gapped? Where are you, where are you, you know, where are you short, and how do you get from How do you close those gaps? Certainly extend Zero Trust data.
I believe that's a biggie. You hit on this quite a bit, Brandon, kind of fusing backup and security. You gotta get over those, those sec- those, those gaps. And, and test, test, test. The one other thing I would say is I love your point on complexity, Brad Tallman, and this is the
thing I absolutely love about what Everpure has done, and I'm not trying to do this to be a fan of Everpure, but this stuff is difficult. It's complex, it's difficult. And what Everpure has done, throughout its entire existence is it's made the difficult really simple. And that's why I think this focus on, you know,
deliver the solutions that are, that, that abstract all of that complexity kind of, are very complete in their coverage, DR deep resilience or protection and resilience. But abstract all of that from those folks that are becoming more and more general in nature, and allows them to use them to effectively, drive, you know, cyber resilience across the organization from products to people and so on and so forth.
But I would really start with that. Understand where your weaknesses are and kind of operate from there. Yeah. And I think the courage to, to give your teams the, the grace, right? Like, they likely aren't all of the culprits of how you got there, right?
Mm-hmm. There really doesn't matter how you got there, it matters how you go forward. You know, we sort of all kind of wound up in this moment with AI together. So I think give, you know, teams that, that, that safety to, to make the mistakes and, and then really, you know No- nobody's testing tomorrow and, like, realizing they've met
their ceiling. Like, "Oh, we can We never have to worry this Evergreen again," right? Yeah. You're usually probably at your floor. So figure out what y- what your ceiling is, and then sort of march towards there and invest in that. A definite common theme by you, just to add
some comments while Brandon If you could pull our, our last couple of slides backup for us. It's having a plan and testing it. And if I think about that, 'cause you guys have both kind of hit on that a few different times, how often are you making changes into your environment? Probably, like, on a daily basis.
You know, sometimes hourly for some organizations, at least monthly. Mm-hmm. So how frequently are you doing that testing? Because when things change, that plan may also have to change. Maybe it doesn't, but you don't know that if you're not constantly reviewing it and not constantly testing it.
Yeah. So as we're starting to wrap this up a little bit, we throw out a couple things. Like, we didn't get a lot of details today, about some of this stuff, about, like, exactly what do you do, but we've got a couple workshops that we run from Everpure. You know, Matt made a great point, or at least in my biased opinion, but you want some
outside influence in what's going on, right? Your teams are great, but they are not actually recovering from ransomware every day, right? So get some perspectives from outside vendors. One great way to do this is through our workshops. We have a nice tabletop workshop.
That's actually really good for you to run internally to pull all the teams together. Have you pulled your infrastructure and security teams? Have you brought somebody from the business? This is not an IT-only problem, right? It's an everybody problem.
So bring everybody in. Let's walk through an attack. Let's expose where some of those gaps might be. And if you're kind of beyond that, everybody gets it, you're looking for a practical thing To do, we have a great workshop about building isolated recovery environments. We can start getting into some, a little bit more practical things that you can do.
So encourage you to reach out to your Everpure, AEs or account executives to do this. These are no-cost things, by the way. We come to you, no cost to you. A little bit of investment of your time is really the only thing. We'd love to run. And if you'd click on the next one, Brad.
Another great thing, join our Everpure digital community, right? Interact, engage out there. Don't just make this a you thing, right? It is a community thing. It takes, you know, an ecosystem of individuals and companies to solve this problem.
Jump in. And of course, if you haven't read Matt's paper, I believe we'll have that out there in kind of the show notes for everybody, that you can go download that. So with that, if there's kind of one point that I think we wanna leave with today, it's that, first of all, AI is a real thing, and it's changing that threat landscape, and it's
doing it faster than pretty much any organization is able to adapt. And that cyber resilience now depends on more than just your traditional perimeter defenses, right? Those just don't work, and pro- probably haven't worked for quite a while. So the organizations that are gonna be best positioned are really the ones that are
treating data protection, data availability, and data integrity as architectural priorities, not as afterthoughts. Matt, Brandon, really wanna thank you both. Really great insights today. Thanks everybody who was able to join us or watch this on replay.
Make sure you talk to us about how we can help you. And if there's any other questions we can do, please reach out. Thanks everybody for your time. Thank you. Thanks.
Matt Kimball
VP & Principal Analyst, Moor Insights & Strategy
Scott Taylor
Director, Cyber Resilience, Everpure
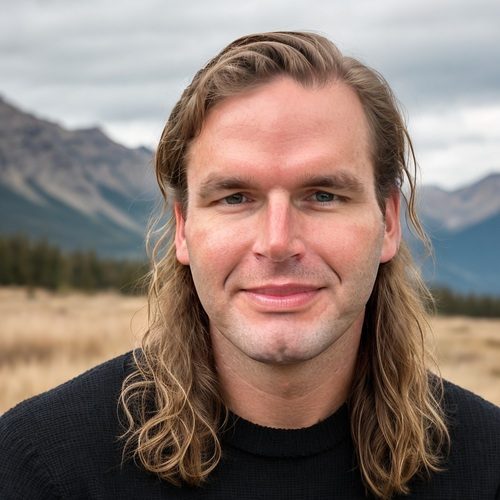
Brandon Willitts
Director Product Management, Cyber Resilience, Everpure
Can your organization recover from cyber incidents quickly and limit operational disruption? Learn how to detect threats earlier, recover faster, and improve operational survivability.
Featuring the latest Moor Insights & Strategy report, this webinar explores how AI-driven cyber threats are forcing CISOs to reframe storage from passive infrastructure to an active resilience foundation. As AI empowers attackers, it also serves as a critical asset for defense.
In this webinar, we’ll examine a strategic framework that integrates AI-powered anomaly detection, immutable snapshots, and rapid cleanroom recovery—showing how to turn your data estate into an active resilience layer.
Key takeaways:
- Align protection, detection, and recovery into a unified operational strategy
- Use storage-layer telemetry as an AI-driven sensor to identify unusual write patterns before they escalate and integrate with security operations for closed-loop response
- Automate and accelerate remediation and recovery to reduce downtime and improve operational survivability
- Implement hardware-enforced immutability to preserve clean recovery points, even during credential compromise
We Also Recommend...
Personalize for Me
My Updates
No updates at this time.